

We receive takedown notices regularly. They come from individuals, lawyers, companies, and governments. This post is part of a series where we document how we handle them, both the routine cases and those that reveal something worth discussing publicly.
This request, to take down icepi.cx (now online again at http://icepicx.is/ ) arrived from a company we have no relationship with, acting for a government agency in a country where we do not operate.
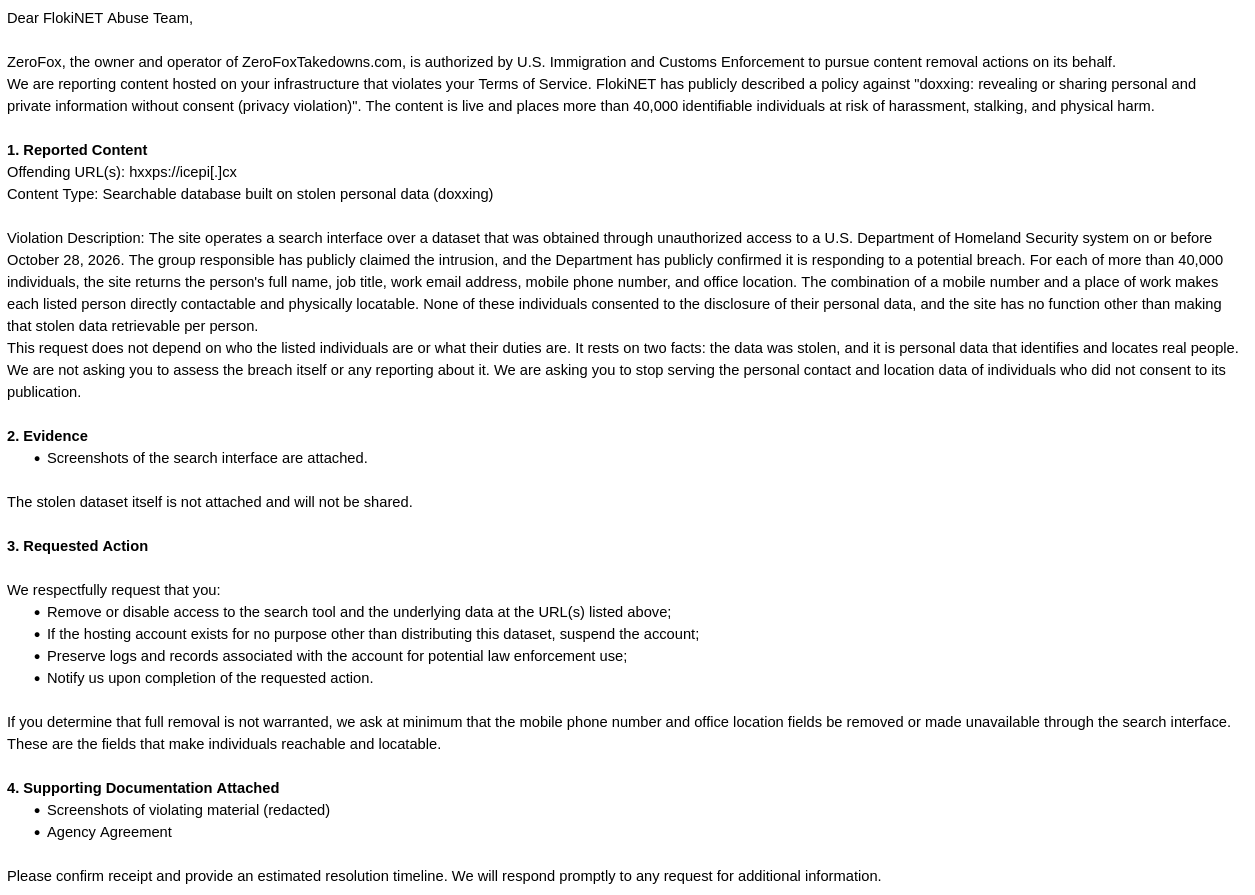
We declined the request.
What happened
The notice describes a doxxing campaign. That is not what the site is.
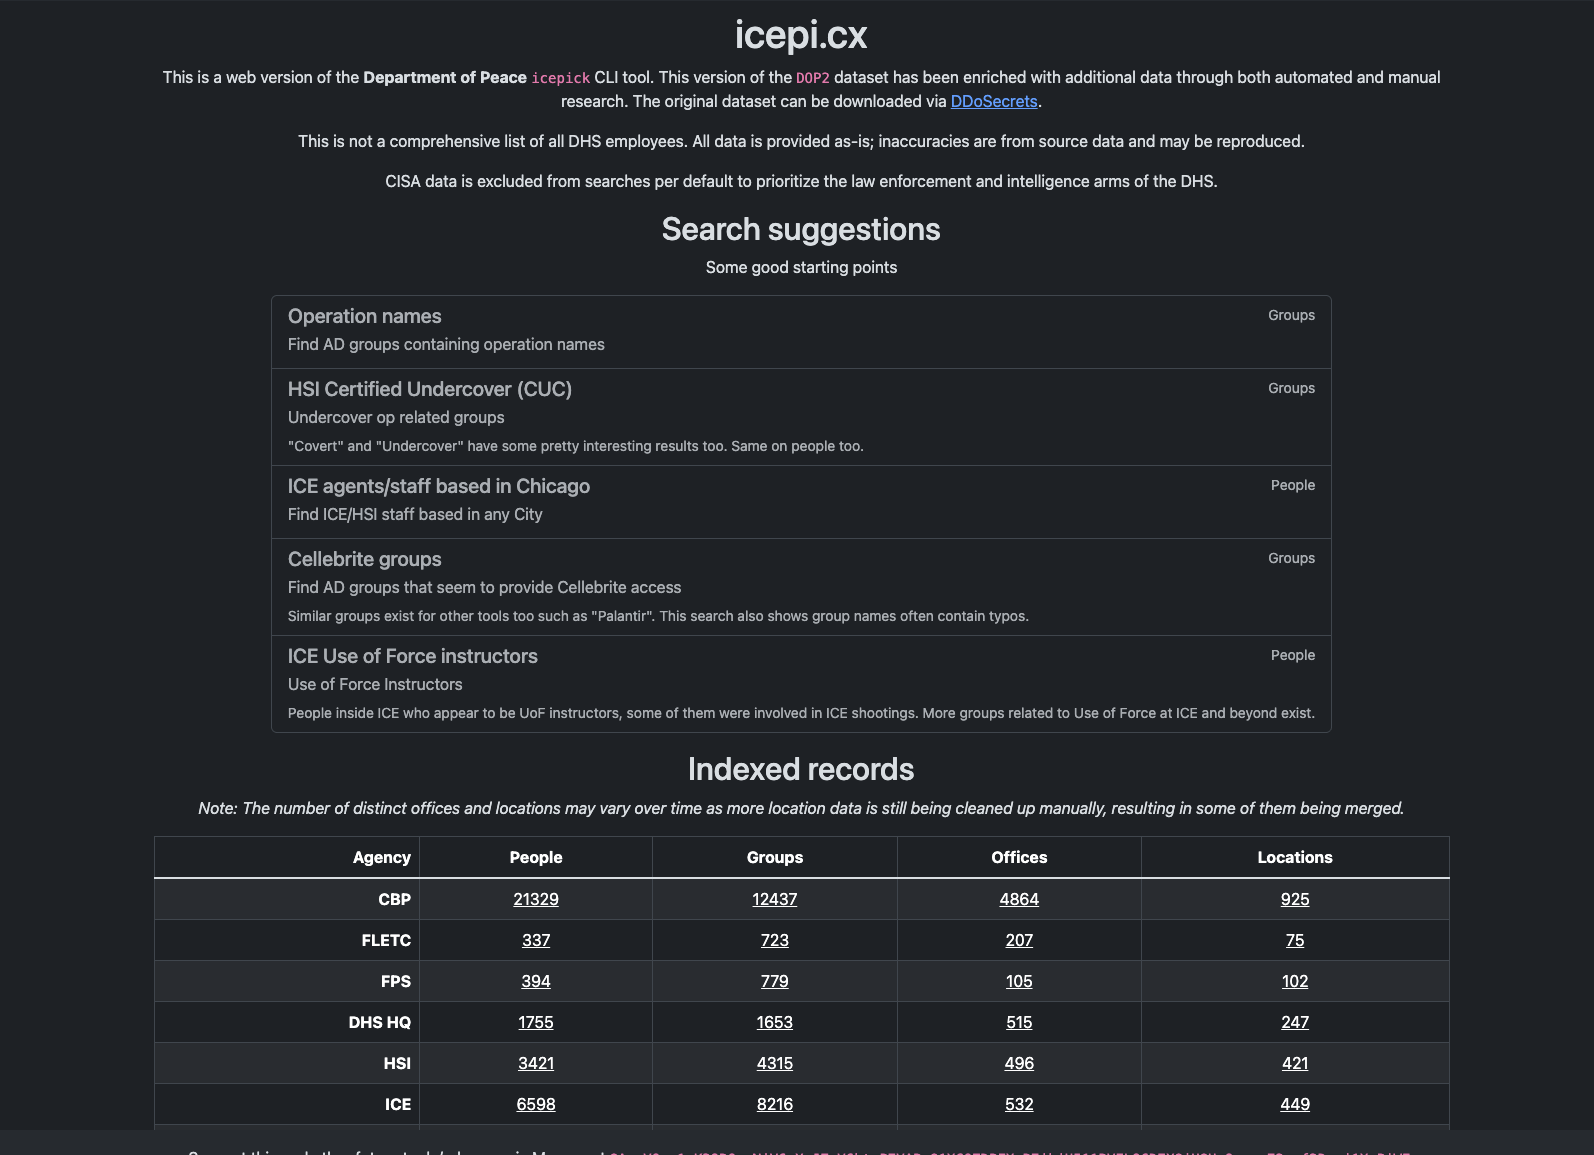
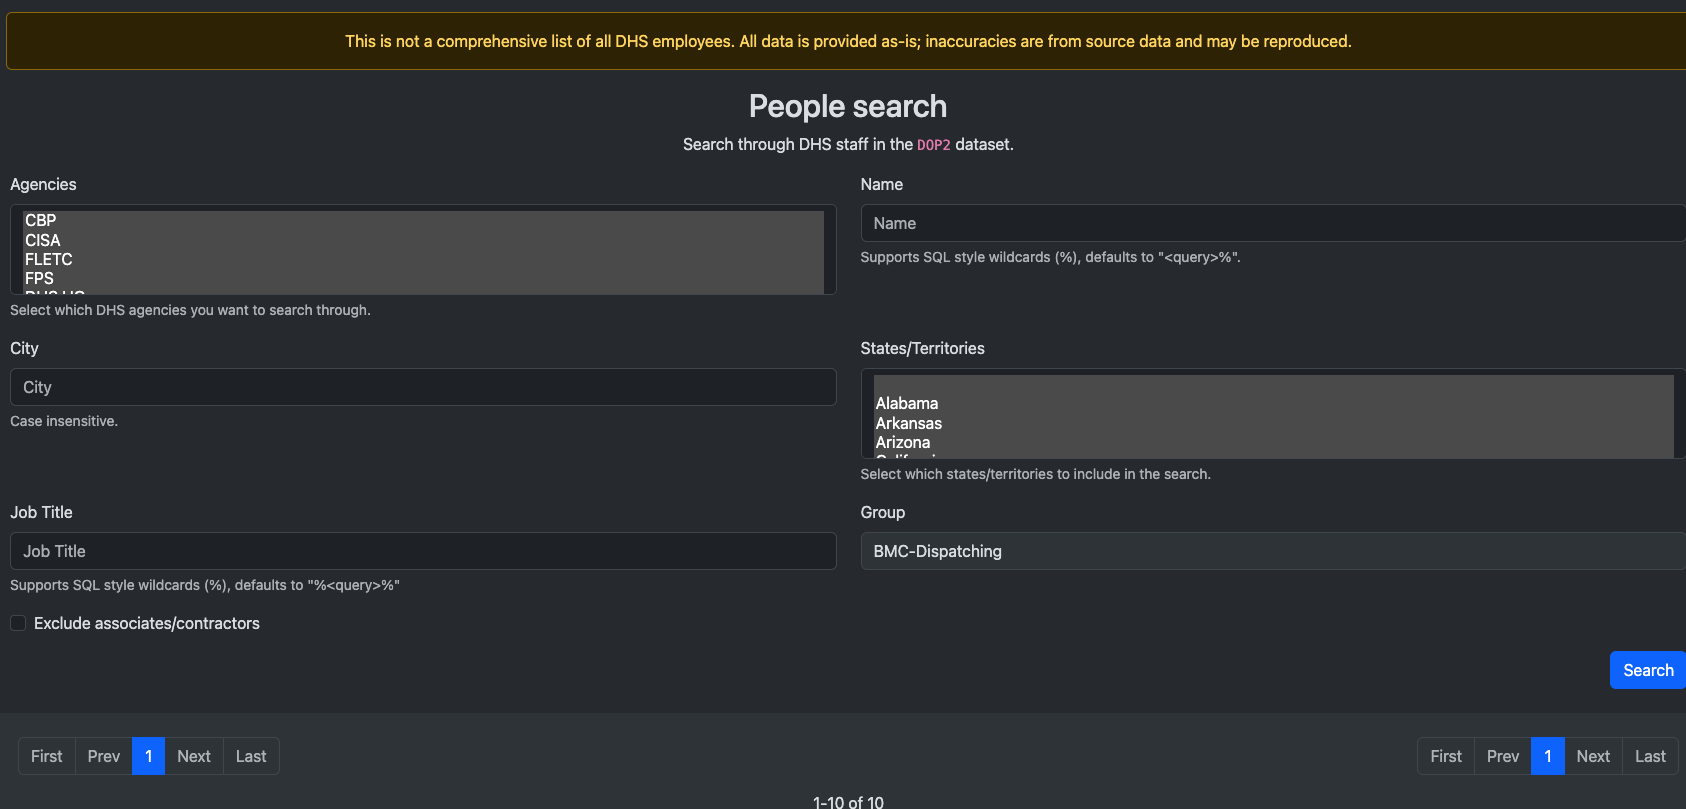
Doxxing publishes private details about private people so that others can find them at home. Icepick publishes work identities of government employees. Who they work for. What their role is. How they can be reached in that role. The information describes people in the exercise of public authority, not in their private lives. Federal officers carrying out an enforcement programme are not private individuals while they are carrying it out. The public has a legitimate interest in knowing who is doing that work, under whose authority, and in which office. Journalists cannot report on an agency whose personnel are structurally unknowable.
We are not pretending the origin of the data is comfortable. It came from a breach, and nobody in the dataset chose to be in it. The question we had to answer was narrower: does publishing it serve a purpose that a hosting provider should protect? We concluded that it does. The site functions as a reference tool for accountability reporting by journalists and citizens, and that is a use we exist to keep online. This is why we declined the take-down request.
Why this matters
An automated takedown notice does not remove the work of checking whether an accusation is true. It moves that work to the recipient. We made that point about a false accusation from a German police authority, and it holds here with a different agency, a different country, and a different kind of claim.
ZeroFox finds candidate material through AI-driven detection. Whether a given site is accountability journalism or a harassment campaign is exactly the judgment that detection cannot make. Someone has to read the site, look at the dataset, and weigh public interest against personal risk and this morning that someone was us.
This case adds something to that. The party accusing us and the party contacting us are no longer the same. We cannot see who inside ICE decided this site should go, whether anyone did, or what they were shown before deciding. We are being asked to validate a claim whose author we cannot identify.
As a business model, none of this is new. Copyright has worked this way for decades. A private company sells monitoring to rights holders, scrapes for matches, sends demand letters automatically, and takes a share of whatever recipients pay to make the letters stop. Volume is the product. Checking is a cost against it. Plenty has been written about what that does to legitimate speech, and most of it transfers to what arrived in our inbox this morning.
What has changed is the client. In this case its a governmental institution, not a private company. DHS signed a $15 million contract with ZeroFox in July 2026 covering ICE and Homeland Security Investigations, and the company can file on the department’s behalf until 2028. The Intercept reported on a leaked memo describing the programme internally as a “Doxing Mitigation Initiative,” and quoted an ICE official who worried it could be turned on whistleblowers and critics inside the agency rather than on threats from outside it. ZeroFox also has form. In 2015 it classified peaceful Black Lives Matter organisers in Baltimore as “threat actors” warranting continuous monitoring, partly on the strength of their follower counts. The FBI hired the company anyway in 2021.
Validation by the recipient is no longer a side effect of a badly built process. It is part of what the service sells. Finding politically and journalistically relevant information is the product, removing it is the deliverable, and the number of notices filed is the measure of success.
What happened to the site?
By mid-morning, icepi.cx no longer resolved. Its registrar, CentralNic, had placed the domain on serverHold.
Our refusal kept nothing online. The request that decided the outcome to take the site down was not the one sent to us. A registrar reached the opposite conclusion the same morning, published nothing, and a global audience lost access to the site. In the meantime the site is online again under a domain from a different registrar (http://icepicx.is/)
What should be done about this
As we describe in our previous article, legislation like the DSA loads obligations onto hosting providers and asks nothing of the people who file notices.
This case demonstrates what can happen once filing becomes a commercial service available to governmental organisations.
Anyone filing a takedown notice on another party’s behalf should have to state who they act for, under what legal basis, and who is accountable if the claim is wrong. Where a notice was produced by automated detection, that should be declared on its face. A provider cannot weigh a claim properly without knowing whether a human ever looked at it.
Removals at the registry and registrar level need the the same scrutiny.
Enforcement against genuinely harmful content is a legitimate goal, and protecting individuals from harassment is a real one. But a system where an agency can buy removals through a contractor, where the contractor is possibly paid by volume, and where the quickest route runs through infrastructure nobody is watching, like the registrar in this case is not a system for stopping harassment. It is a system for making inconvenient information disappear.
What others write about this case
https://subscriber.politicopro.com/article/2026/10/ice-dhs-leak-takedown-request-01140645
